

PRISM Vanguard
Vulnerability management that takes the report seriously.
One scanner finds vulnerabilities. Vanguard decides which ones matter. From discovery through CVE correlation and EPSS/KEV prioritisation to SLA-tracked remediation and a finished client report — calibrated, traceable, without alert noise. Self-hosted, AI and hosting in Germany.
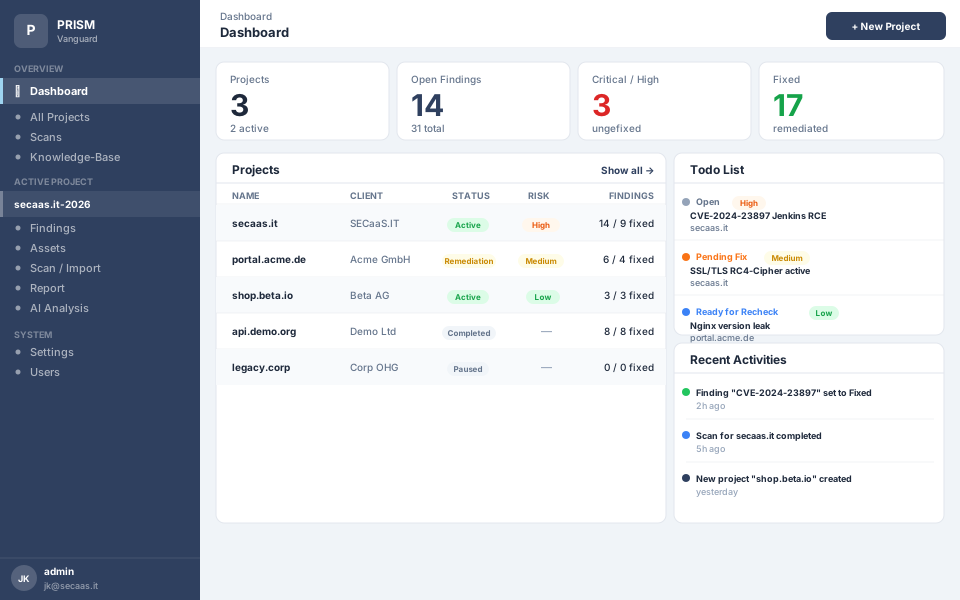
The scanner finds 400 criticals.
Of those, 12 are actually exploitable. The rest the ticket system writes off as false positives three months later.
Priority by CVSS score.
CVSS 9.8 — no exploit in the wild, not reachable from outside, legacy system being decommissioned in 2025. Still at the top.
The annual pentest is done.
Nine months later. New CVEs, changed infrastructure, no re-scan. The picture from March is no longer the picture from now.
Vanguard addresses all three — calibrated, continuous, traceable.
Calibration
Why Vanguard is different.
The raw finding is cheap. The classification is the work. Every scanner produces Criticals — Vanguard checks whether they actually are: legacy signatures on modern infrastructure are defused, attack types correctly named (a DoS is not an RCE), exploitation prerequisites listed at the finding, catch-all/soft-404 phantoms removed.
What remains is a short list of real risks instead of a long list of assumptions — traceable down to individual lines, without rework at the client.
Device classes
A scanner sees an IP. Vanguard sees a device.
Vanguard identifies from the scan whether an address is a Synology, a FRITZ!Box, a Proxmox host or a printer — and names the right patch path: DSM/firmware update instead of "apt for everything". On firmware-managed appliances it additionally defuses banner CVE false positives that arise when a vendor backports fixes without incrementing the version number.
Synology NAS
→ DSM update
FRITZ!Box
→ Firmware
Proxmox
→ PVE update
Printer / IoT
→ Device scanner
Pipeline
One tool for the full journey.
Five tools and a spreadsheet. Or one platform. Recon, scan, calibration, prioritisation, and report run in one place — what is scanned lands in the same report as what is prioritised.
OSINT and subdomain enumeration: PRISM Vanguard maps your attack surface — assets, subdomains, open ports, exposed services. Everything in one place before the first scan runs.
What PRISM Vanguard includes
- Complete pentest workflow: planning → scan → findings → report → follow-up
- Calibrated severities, fewer false positives: traceable rules the admin maintains without a release
- Device class detection: NAS/router/Proxmox/printer automatically identified — device-specific patch path instead of "apt for everything"
- Customisable calibration ruleset: own signatures and rules maintainable — without a software update
- CVE correlation via NVD: automatically match product versions against known vulnerabilities
- EPSS + CISA-KEV: prioritise by real exploit probability, not gut feeling
- CSAF advisory matching & early warning: matching against BSI CERT-Bund, CISA and Red Hat advisories — alert when a new advisory hits your own inventory
- Continuous attack-surface monitoring: new subdomains, ports or endpoints trigger an automatic alert — not just on the audit date
- Authenticated scans: store credentials securely, Vanguard scans behind the login too
- Extended asset discovery: exposed cloud storage buckets (S3, GCS, Azure Blob) and SMB/NFS shares — strictly read-only
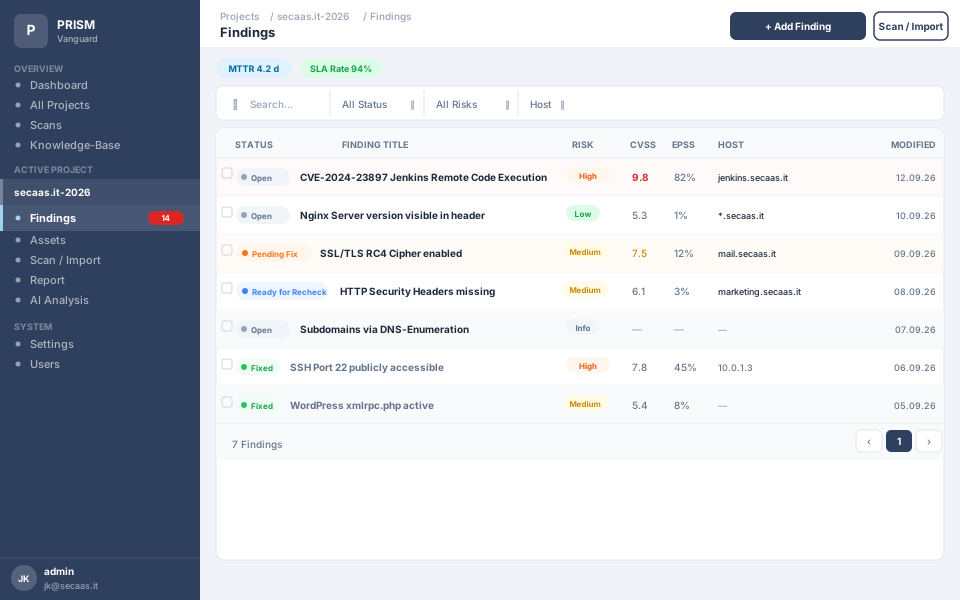
- Retest with delta report: a retest shrinks the report — fixed/new/still open at a glance
- Engagement profiles: from passive recon to deep audit — scan depth and pace selectable per engagement
- SLA tracking: MTTR, SLA rate, and overdue alerts — documented, not estimated
- AI analysis: finding assessment and remediation suggestions, AI local — data stays in-house
- Report generator & Jira export: reports (PDF/DOCX) at the click of a button, findings directly as Jira tickets
- Continuous VM: self-healing re-scan — ongoing operations, not just the annual pentest
- True multi-tenancy: multiple clients and projects in parallel, with strict access separation per tenant
Sovereign and audit-proof.
Your vulnerabilities stay yours. Self-hosted, AI evaluation local, hosting in Germany — finding data never leaves the building. Every assessment is justified and traceable down to the rule, no blackbox score. Built for KRITIS, NIS-2, and regulated environments where "trust us" is not an answer.
Who is PRISM Vanguard for?
Security consultants
Multiple client projects in parallel, reports and findings that the client tracks themselves.
Internal security teams
Vulnerability management as an ongoing discipline — not just once a year.
CISOs & IT leadership
The risk portfolio at a glance — what is open, what is overdue, where is the pressure.
On a real project, not on slides.
In the initial call we show scan, calibration, CVE correlation and report on a real pentest — not a demo slide.