

TISAX (VDA ISA 6.0)
TISAX proof for the automotive supply chain.
An OEM or Tier-1 customer requires a TISAX label as a prerequisite for collaboration. PRISM ISO covers the complete audit workflow — with AI assessment of your policies and an auditor you can book directly.
Who it's for
Suppliers and service providers to the automotive industry who have been requested by an OEM or Tier-1 partner to undergo TISAX assessment — regardless of assessment level.
Already running an ISO 27001 certification? One control counts for both standards.
AI Policy Assessment
What's missing — per TISAX requirement, not in general.
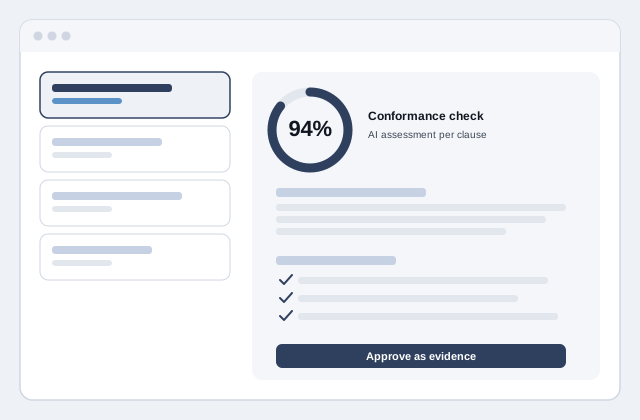
PRISM reads your existing policies and shows, for each VDA ISA requirement, what is covered and what is specifically missing — with the expected scope per chapter.
What you get
What PRISM brings for TISAX
-
Complete TISAX Audit Workflow
VDA ISA 6.0, all assessment levels — from planning to proof in a single system.
-
Controls & Gap Analysis
Information security across the supply chain: every requirement assessed, gaps concretely identified.
-
AI Policy Assessment
PRISM reads your policies and shows, for each TISAX requirement, what is covered and what is missing.
-
Multi-Framework Mapping
Fulfil controls for TISAX once — automatically reuse them for ISO 27001.
-
Automatic SoA
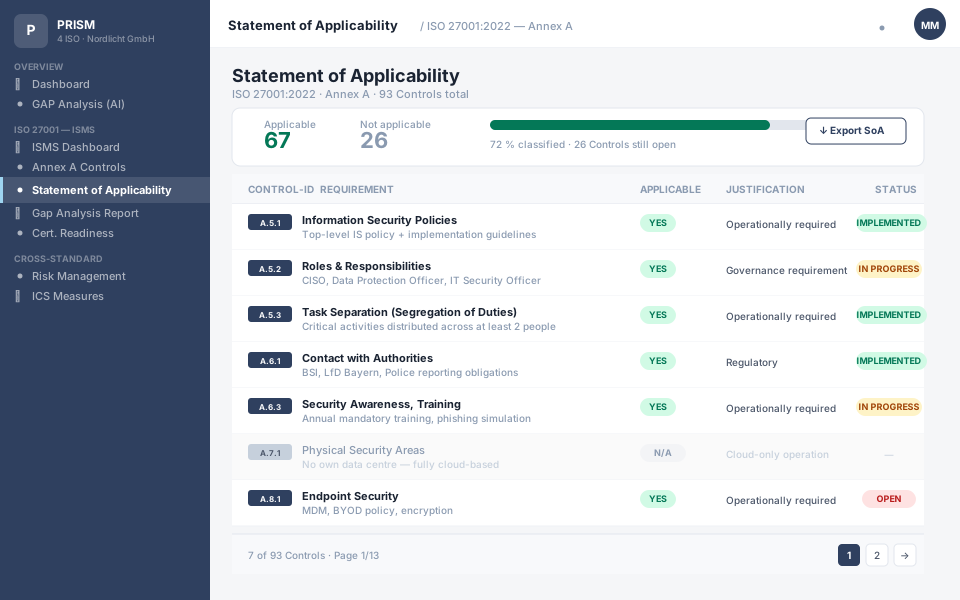
The Statement of Applicability is generated directly from your assessments — ready for audit.
-
Auditor Directly Bookable
Once you are ready for certification, book the auditor directly without any coordination overhead.
TISAX Assessment Preparation
TISAX proof: structured, not as a time-and-materials consultancy project.
TISAX (VDA ISA 6.0) requires a structured ISMS for the automotive supply chain. PRISM ISO covers all requirements across all three assessment levels — with SoA, gap analysis and remediation plan for ENX Association auditors.
Frequently asked questions about TISAX
- What is TISAX?
- TISAX (Trusted Information Security Assessment Exchange) is an information security assessment standard specifically for the automotive industry, developed by the VDA. It is based on VDA ISA 6.0 (closely aligned with ISO 27001) and is required by OEMs and Tier-1 suppliers as a prerequisite for project involvement.
- Who is TISAX mandatory for?
- TISAX is required for companies in the automotive supply chain that process sensitive information from OEMs (e.g. BMW, Mercedes, Volkswagen, Porsche, Audi) — design plans, prototype photographs, customer data or vehicle development documents. Anyone wishing to operate as a supplier needs TISAX.
- What are the TISAX assessment levels?
- TISAX distinguishes three assessment levels: Level 1 (self-assessment, no external audit), Level 2 (assessment by an accredited audit service provider, no physical site visit), Level 3 (comprehensive assessment with physical site visit — for the highest protection requirements such as prototypes). The OEM determines the required level.
- How long does TISAX certification take?
- With PRISM ISO and a structured approach, companies are typically assessment-ready within 3–6 months. The availability of the audit service provider can influence the timeline. Starting with the right approach avoids common mistakes and rework cycles.
- How does TISAX relate to ISO 27001?
- TISAX is strongly based on ISO 27001 — companies that are already ISO 27001 certified have already fulfilled the majority of TISAX requirements. PRISM ISO includes a TISAX–ISO 27001 crosswalk: fulfil controls once, use them for both standards. TISAX-specific additional requirements (protection levels, prototypes, customer data) are recorded separately.
Software only — or with advisor and auditor?
Three tiers, one goal: your TISAX label. From the licence to the fixed-price package with auditor included.
So geht PRISM vor
Von der Lücke bis zum laufenden Betrieb.
Vier Phasen, eine Plattform — kein Wechsel zwischen Tools, keine Lücken zwischen Phasen.




Wo stehen Sie heute?
PRISM bewertet Ihre bestehenden Dokumente, Prozesse und Kontrollen gegen alle Anforderungen der TISAX. Jede Lücke kommt mit Begründung und direktem Link zur Maßnahme — kein manuelles Zusammensuchen.
Was unsere Kunden sagen
„Der Security Health Check war sehr effizient und zielführend und half uns, Transparenz zu schaffen."
Johannes Beier
IT-Leiter · B2B Medical
Security Health CheckTrusted by











Show us your TISAX request.
In the initial call we clarify concretely which assessment level you need and how long it takes.