

SOC 2 Type II
The proof US customers want to see.
A security questionnaire or enterprise contract requires SOC 2 — often in parallel with ISO 27001 or C5. PRISM ISO gets you to proof in an average of 3 months, with controls you reuse for every additional standard.
Who it's for
Founder or CTO of a SaaS company, 20–150 employees, with a US-heavy customer base or investor requirements. Operating in Europe in parallel? BSI C5 is often required too — with PRISM both are covered in one pass.
"How fast really?" — in an average of 3 months, with clear milestones.
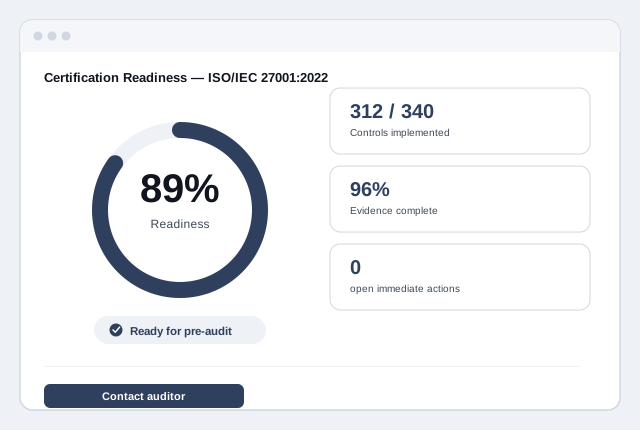
Certification Readiness
Know where you stand for SOC 2 — at any time.
PRISM shows your SOC 2 readiness per Trust Services Criterion — including AI assessment of your policies, a tamper-proof evidence history and a direct link to the auditor when you are ready for certification.
What PRISM brings for SOC 2
- Controls, gap analysis and Statement of Applicability for SOC 2 Type II
- AI assessment of your policies against the AICPA Trust Services Criteria
- Multi-framework mapping: reuse controls for ISO 27001, BSI C5 or NIS 2
- Internal audit and management review directly in the platform
- Tamper-proof change history — the evidence a US auditor expects
- Auditor directly bookable once you are ready for certification
German customer additionally asking for C5?
The multi-framework mapping fulfills controls once and applies them automatically to every additional standard — no double effort between US and DE requirements.
Software only — or with advisor and auditor?
Three tiers, one goal: your SOC 2 proof. From the licence to the fixed-price package with auditor included.
So geht PRISM vor
Von der Lücke bis zum laufenden Betrieb.
Vier Phasen, eine Plattform — kein Wechsel zwischen Tools, keine Lücken zwischen Phasen.




Wo stehen Sie heute?
PRISM bewertet Ihre bestehenden Dokumente, Prozesse und Kontrollen gegen alle Anforderungen der SOC 2. Jede Lücke kommt mit Begründung und direktem Link zur Maßnahme — kein manuelles Zusammensuchen.
Was unsere Kunden sagen
„Der Security Health Check war sehr effizient und zielführend und half uns, Transparenz zu schaffen."
Johannes Beier
IT-Leiter · B2B Medical
Security Health CheckTrusted by











Show us your security questionnaire.
In the initial call we clarify concretely what is missing for SOC 2 and how long it takes.