

PRISM ISO
The ISMS platform that truly understands your policies.
ISO 27001, NIS 2, C5, SOC 2, TISAX and 10 further standards in one platform. The AI reads your policies, evaluates them chapter by chapter against the standard and shows concretely what is missing — with an expectation horizon for every point. Hosting and AI processing exclusively in Germany.
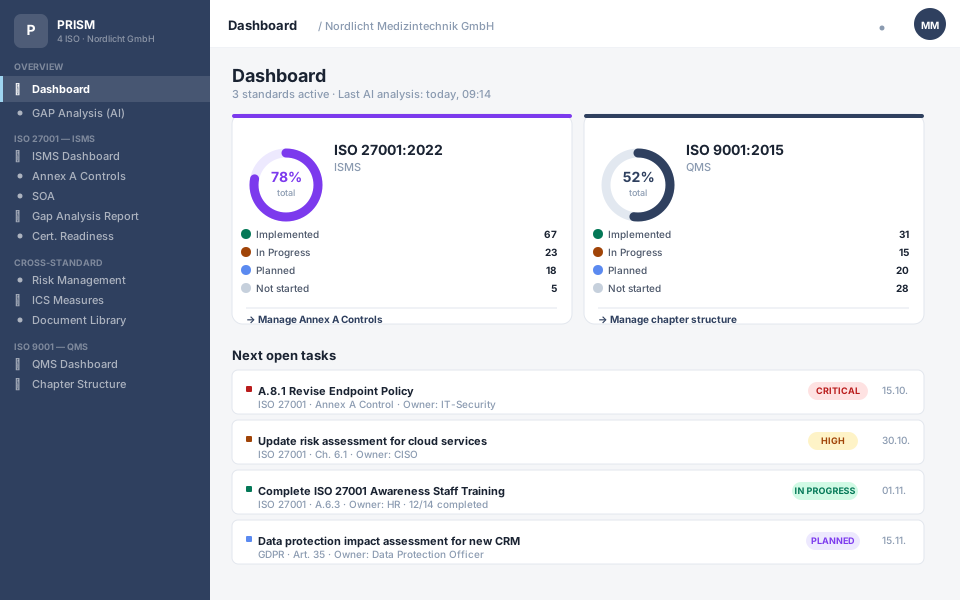
- ISO 27001 · NIS 2 · C5
- SOC 2 · TISAX and 8 further standards
- Avg. 3 months
- average time to certification
- Hosted in Germany
- software and data on German servers
- Fixed price & date
- no day rates, no open end
Why PRISM ISO
What sets PRISM ISO apart.
Built from audit experience
Every feature in PRISM comes from real audit practice: what does the auditor actually want to see for each standard chapter? This question brings capability, gap and quality together — the result is not a one-size-fits-all ISMS, but a management system optimally tailored to your organisation.
Tailored to your organisation
No one-size-fits-all ISMS. PRISM identifies your processes, scopes and assets — the management system is built from your actual starting point.
AI-native — not bolted on
PRISM AI is built into every compliance process: assessing policies, identifying gaps, recalculating risks, measuring readiness — not connected via an external API.
ISMS operations after certification
The ISMS stays alive: surveillance audits, incident management, continuous improvement and follow-ups — all in the same platform that accompanied the implementation.
How PRISM ISO works
Implementation. Operations. One platform.
Choose the phase — and see which steps PRISM handles.
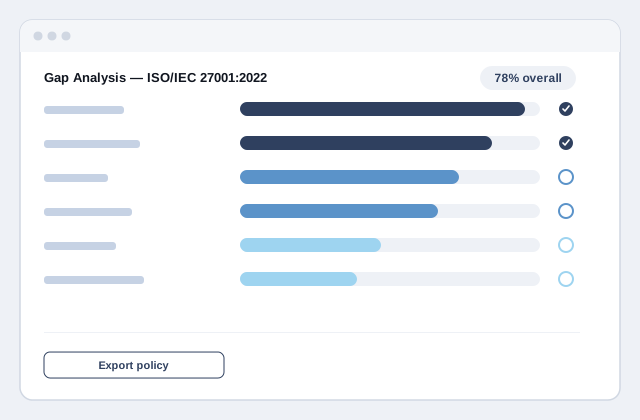
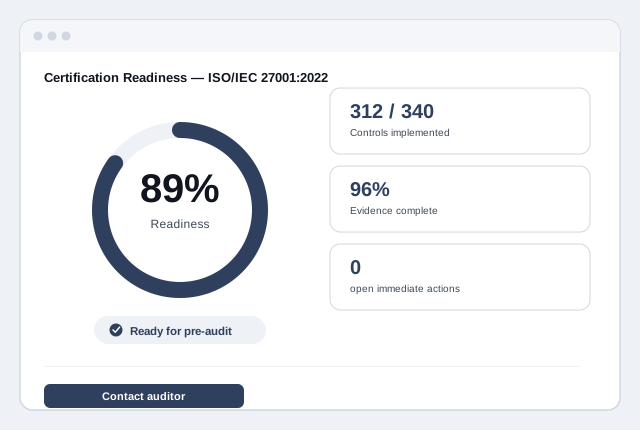
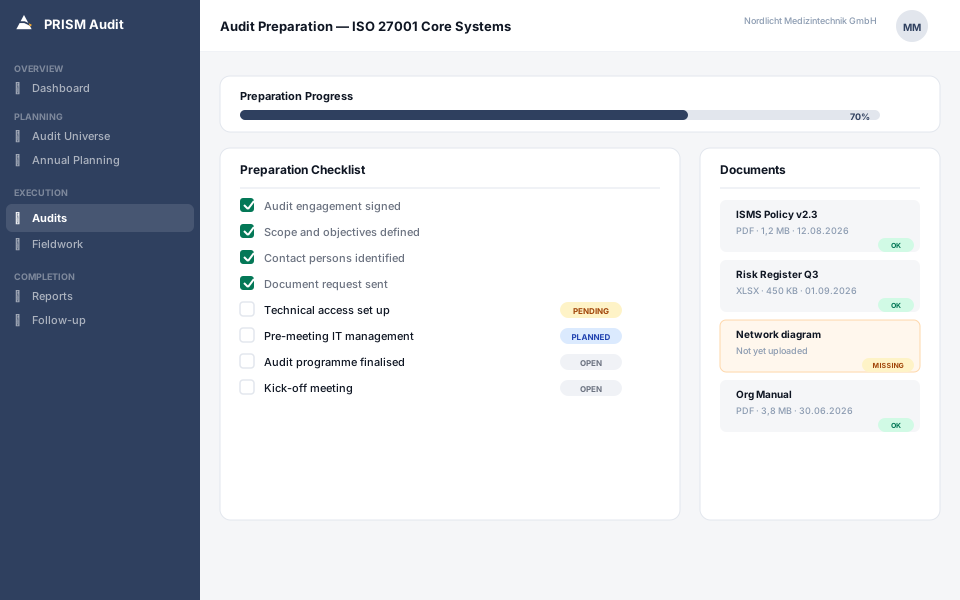
What the AI in PRISM specifically does.
Not ChatGPT bolted on via an API — PRISM AI is built into every compliance process. This is how it works.
Read
What the AI analyses
- Policies, process descriptions and documents of all kinds — in any format
- Bulk analysis of entire document sets at once
- Use existing material — no need to rewrite before analysis
- Policy AI check: missing roles and requirements are automatically flagged
Assess
What it evaluates
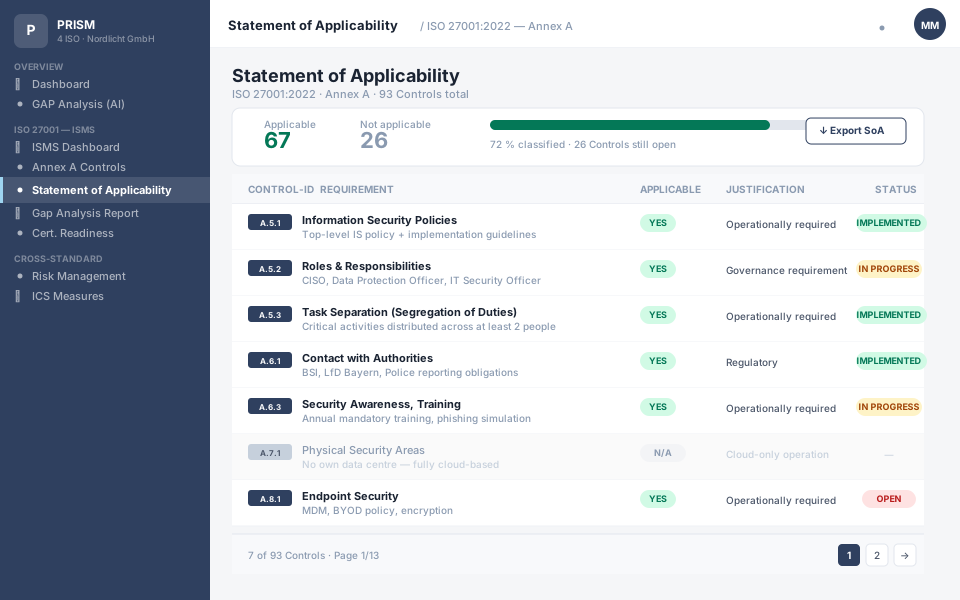
- All normative requirements of ISO/IEC 27001:2022 — Clauses 4–10 with all subclauses and all 93 Annex A controls
- Expectation horizon: what the auditor specifically wants to see for each requirement
- What is fulfilled, what is missing, what needs improving — with justification
- Automatic risk re-assessment when actions or context change
Deliver
What it returns
- Gap report and readiness score based on real system data
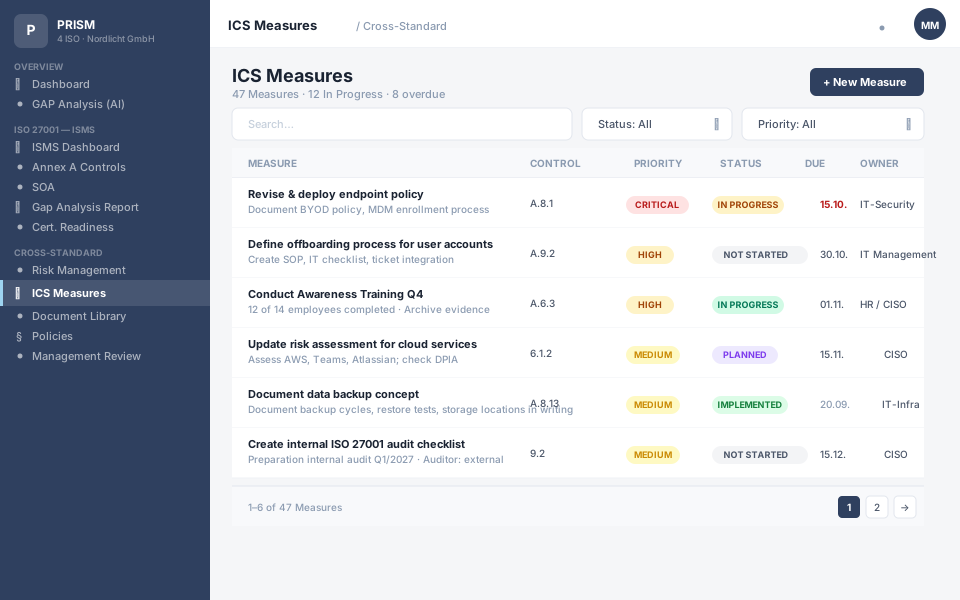
- Prioritised action recommendations — ordered by impact and urgency
- Score override with mandatory justification and audit trail — no black box
- AI fallback chain: if one provider fails, the next takes over automatically
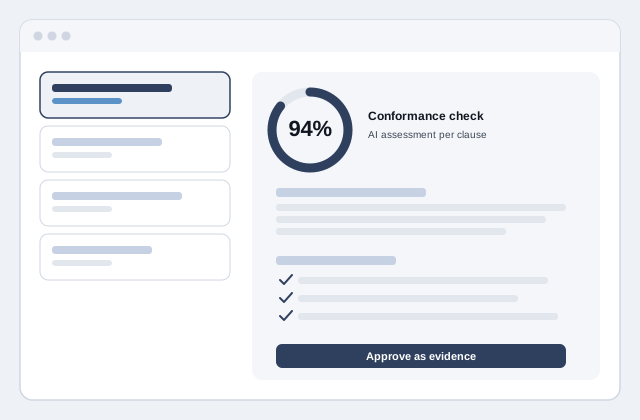
Control Evidence
How evidence is documented in PRISM.
Compliance is evidence. PRISM closes the gap between action and proof — no parallel filing, no system breaks.
-
Upload evidence documents directly
Proofs, logs, screenshots — attached directly to the action or control, not in a separate filing system.
-
Control approval workflow
Approve and document controls after implementation with a four-eyes principle — with timestamp and owner.
-
Tamper-proof change history
Every status change, every override, every AI assessment is immutably logged — retrievable for the auditor.
-
Auditor sharing without access
Share selected documents directly with external auditors — without giving them a PRISM account.
-
DOCX and ZIP export
Export policies, SoA and control evidence as a Word document or Markdown ZIP — at the push of a button, audit-ready.
Integrations & API
Integrating PRISM into your system landscape.
REST API, Confluence Connector, OAuth2 — PRISM fits into existing infrastructures rather than becoming another island.
REST API (fully documented)
liveAll data and processes in PRISM controllable via API — read controls, create actions, query status. For custom dashboards, SIEM integrations and automations.
Confluence Connector
liveRead Confluence pages directly as document sources and have them AI-analysed. No manual export/import — changes in Confluence become visible in PRISM.
OAuth2 / API Keys
liveSecure system-to-system communication via Client Credentials Flow (OAuth2) or API keys for machine users — no user interaction, no shared passwords.
On-Premise Option
livePRISM runs on your own infrastructure — Docker-based, fully self-hosted. AI processing stays on your server. No cloud required.
Planned: webhooks (event-driven), AD/LDAP sync, Wazuh security events → ISMS.
What you get in concrete terms
What PRISM ISO includes
-
ISO/IEC 27001:2022 including migration path
Latest standard version including transition path from 2013 — no restart, just continuation.
-
Multi-framework in a single pass
Fulfil controls once, automatically reuse for C5, SOC 2, NIS 2 and more — no double effort.
-
Bulk document analysis
AI-assess entire document sets at once — instead of working through document by document manually.
-
Practice library from hundreds of projects
Over 80 templates and guidelines from real projects — immediately usable, fully customisable.
-
Multi-tenancy & MSP mode
Multiple tenants in one instance — for hospital groups, MSPs and consulting firms managing multiple clients.
-
Tamper-proof and audit-ready
Seamless change history and report generation at the push of a button — for auditor, management and data protection officer.
All 132 live features in detail: PRISM feature overview →
All standards & regulations in one platform
Multi-framework mapping: fulfil controls once, reuse them for every additional standard — your management system grows with your customers' requirements.
Your standard not listed? We add new frameworks at short notice — get in touch.
Choose the right starting point
Software only — or with advisor and auditor?
PRISM ISO is the platform. How much support you want is up to you.
PRISM Guided
With advisor, without surprises.
Software plus advisors who have been this way many times before. Scoping, SoA, reviews and audit preparation in one package. Fixed price, payable monthly.
- ✓ Advisor support (package person-days)
- ✓ Scoping, SoA and reviews
- ✓ Preparation for the audit
PRISM Certified
Fixed price. Date. Certificate.
Advisor and auditor in one package. You get a fixed price and a binding date — 100% success rate across all implementations · as of 09/2026.
- ✓ Everything from Guided
- ✓ Auditor booked directly
- ✓ Fixed price with defined outcome
Compare all packages: secaas.it/packages →
See PRISM ISO with your own policies.
Bring a policy — in the initial call we evaluate together what the AI assessment makes of it.