

NIS 2
NIS 2 — compliance in 3 months, not 3 years.
The EU directive is in force, fines are coming. With PRISM ISO you fulfil the NIS 2 requirements systematically — with a German auditor at the push of a button. 200+ organisations already manage their evidence in PRISM.
Why now
- • Received a BSI notification? Start here.
- • Customer audit asking for NIS 2 proof?
- • Cyber insurance requiring a compliance certificate?
BSI registration is underway — notices are arriving. Around 18,000 companies in Germany are affected.
Measures Tracker
All 10 NIS 2 areas — as executable measures.
NIS 2 requires evidence across 10 areas. PRISM translates each area into concrete measures with owners, deadlines and audit-proof completion evidence — report-ready for auditor and BSI.
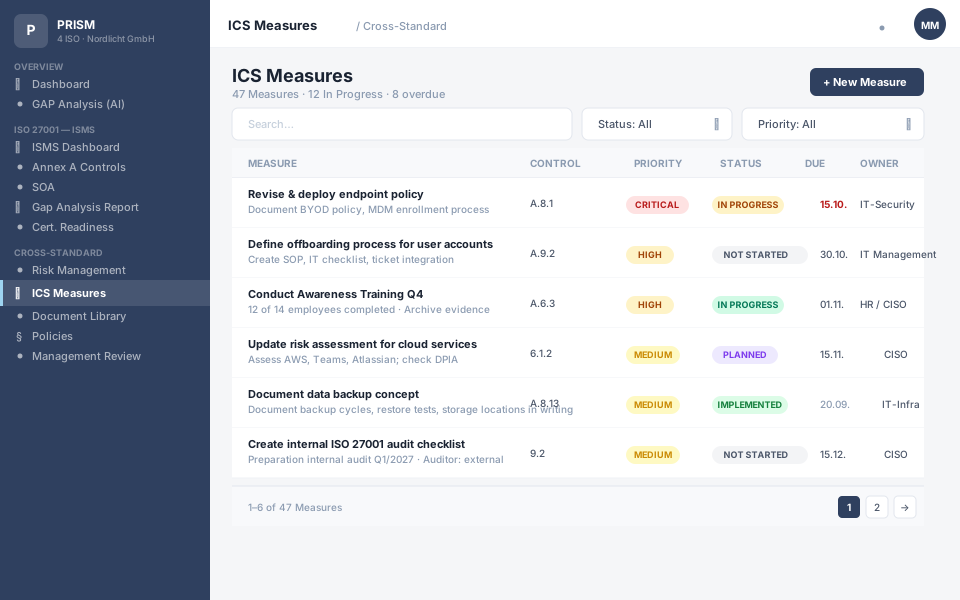
What PRISM brings for NIS 2
- NIS 2 measures catalogue: all mandatory measures as executable tasks
- Gap analysis — current status captured in under 2 hours
- Measures tracker with owners, progress documented and traceable
- Auditor directly bookable (PRISM Certified)
- C5 crosswalk: fulfil NIS 2 and BSI C5 in one pass
- Hosting and AI processing exclusively in Germany
Who is this for?
Yes, if
- 50–500 employees, NIS 2 sector
- IT manager or CISO responsible, no in-house GRC department
- BSI notice or customer audit as trigger
- Goal: evidenceable in under 6 months
Not suitable
- Large enterprises with their own GRC stack (Archer, ServiceNow)
- Pure consulting relationship without software use
Many NIS 2 obligors also fall under BSI C5 — with the integrated C5 crosswalk you fulfil both standards without duplicating effort.
Frequently asked questions about NIS 2
- Am I affected by NIS 2?
- NIS 2 applies to organisations in 18 sectors — including energy, transport, healthcare, digital infrastructure and public administration. In Germany around 18,000 companies are subject to mandatory BSI registration. As a rule of thumb: essential and important entities with 50 or more employees in NIS 2 sectors fall under the obligation.
- What exactly do I need to demonstrate under NIS 2?
- NIS 2 requires measures in 10 areas: risk analysis, incident response, business continuity, supply chain security, network and system security, vulnerability management, cryptography, access control, multi-factor authentication and training. PRISM ISO maps all 10 areas as executable measures — with an evidence report for the auditor and BSI.
- How long does NIS 2 implementation take?
- With a structured tool like PRISM ISO, organisations are typically evidenceable in 3 months — from the first gap analysis to a secured status. Classic consulting projects take 12–18 months and cost many times more.
- What are the penalties for non-compliance with NIS 2?
- The NIS 2 fine regime is strict: up to 10 million euros or 2 % of global annual turnover — whichever is higher. For essential entities, managing directors can be held personally liable.
- Can I cover NIS 2 and ISO 27001 at the same time?
- Yes. PRISM ISO includes an ISO 27001 crosswalk for NIS 2: organisations already pursuing or holding an ISO 27001 certification cover around 70 % of NIS 2 requirements. For companies also subject to BSI C5, the same applies — implement once, demonstrate three standards.
Software only — or with advisor and auditor?
Three tiers, one goal: your NIS 2 proof. From the licence to the fixed-price package with auditor included.
So geht PRISM vor
Von der Lücke bis zum laufenden Betrieb.
Vier Phasen, eine Plattform — kein Wechsel zwischen Tools, keine Lücken zwischen Phasen.




Wo stehen Sie heute?
PRISM bewertet Ihre bestehenden Dokumente, Prozesse und Kontrollen gegen alle Anforderungen der NIS 2. Jede Lücke kommt mit Begründung und direktem Link zur Maßnahme — kein manuelles Zusammensuchen.
Was unsere Kunden sagen
„Der Security Health Check war sehr effizient und zielführend und half uns, Transparenz zu schaffen."
Johannes Beier
IT-Leiter · B2B Medical
Security Health CheckTrusted by











NIS 2 compliance in 3 months.
In the initial call we clarify concretely where you stand and which measures take effect first.