

ISO 9001:2015
Quality management without building a second system.
Already running a management system for ISO 27001 or another standard? PRISM ISO maps ISO 9001 onto it, instead of requiring a parallel structure — in an average of 3 months to certification.
Who it's for
Companies that already operate a management system (e.g. ISO 27001) and need to demonstrate an additional quality management certificate to their customers — tenders frequently require both.
No management system yet? Start with ISO 27001 — ISO 9001 can be mapped later.
What you actually get
What PRISM brings for ISO 9001
-
Controls & gap analysis for ISO 9001:2015
All QMS requirements as actionable tasks — gaps identified concretely, not generically.
-
No parallel build-up
ISO 9001 is mapped to your existing management system — no second system, no duplicate documentation.
-
AI policy assessment
PRISM reads your existing policies and evaluates them against every QMS requirement.
-
Multi-framework mapping
Fulfil controls for ISO 27001 once — automatically reused for ISO 9001.
-
Internal audit and management review
Directly in the platform — audit-proof and without an extra tool.
-
Auditor directly bookable
Once you are ready for certification, simply add the auditor without any coordination overhead.
Multi-Framework Mapping
ISO 9001 mapped to your existing management system — no parallel build-up.
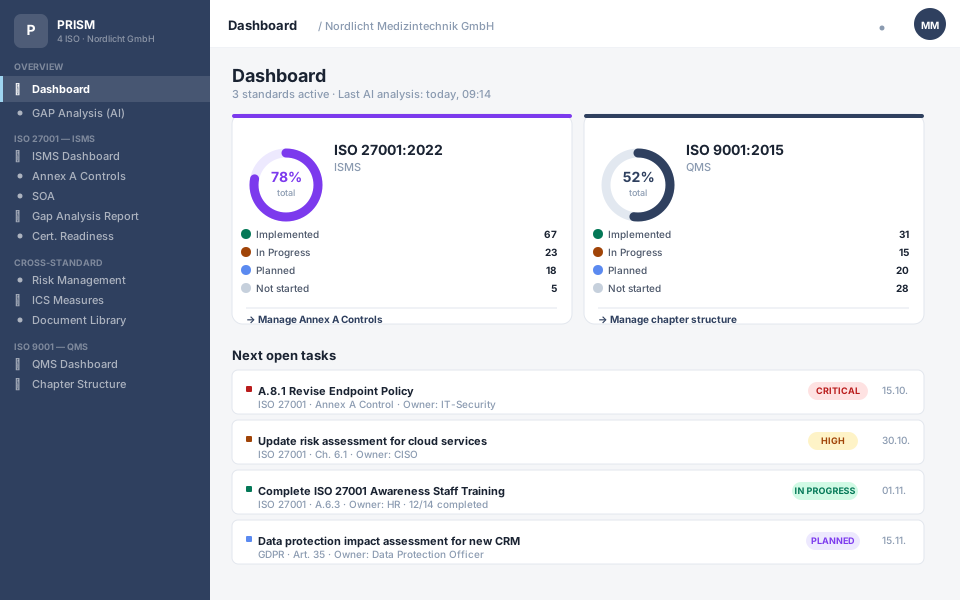
If you already run ISO 27001, the bulk of the work is already done. PRISM ISO maps ISO 9001 to your existing controls — duplicate effort is eliminated and your certification progress remains visible.
Frequently asked questions about ISO 9001:2015
- Who is ISO 9001 relevant for?
- ISO 9001 is the world's most widely adopted standard for quality management — relevant for organisations of any size that need to demonstrate a quality certificate to their customers or public-sector clients. ISO 9001 frequently appears as a requirement in tenders, often alongside ISO 27001.
- Do I need to build a new system?
- No. PRISM ISO maps ISO 9001 onto your existing management system — whether that is ISO 27001 or another standard. Controls you have already maintained are automatically reused for QMS requirements. No second document tree, no parallel tool.
- How long does ISO 9001 certification take?
- With a structured tool and an already-running management system, organisations are typically ready for certification in 3 months — from the first gap analysis to the audit. The timeline depends on the existing maturity level; well-prepared organisations can move faster.
- Can PRISM cover ISO 9001 and ISO 27001 simultaneously?
- Yes. The multi-framework crosswalk in PRISM ISO automatically transfers controls fulfilled once into multiple standards. ISO 9001 and ISO 27001 share many requirements around roles, responsibilities, document control, and internal audits — these only need to be fulfilled once.
- What are the costs for certification?
- Certification costs depend on company size, scope, and certification body. PRISM ISO offers three tiers: Self-Managed (software), Guided (with consultant support), and Certified (auditor at a fixed price, included). We will clarify the specific costs in the initial consultation.
Software only — or with advisor and auditor?
Three tiers, one goal: your ISO 9001:2015 certificate. From the licence to the fixed-price package with auditor included.
So geht PRISM vor
Von der Lücke bis zum laufenden Betrieb.
Vier Phasen, eine Plattform — kein Wechsel zwischen Tools, keine Lücken zwischen Phasen.




Wo stehen Sie heute?
PRISM bewertet Ihre bestehenden Dokumente, Prozesse und Kontrollen gegen alle Anforderungen der ISO 9001. Jede Lücke kommt mit Begründung und direktem Link zur Maßnahme — kein manuelles Zusammensuchen.
Was unsere Kunden sagen
„Der Security Health Check war sehr effizient und zielführend und half uns, Transparenz zu schaffen."
Johannes Beier
IT-Leiter · B2B Medical
Security Health CheckTrusted by











Show us your existing system.
In the initial call we clarify concretely what additional steps are needed for ISO 9001.