

ISO/IEC 42001:2023
AI governance, without building a second system.
Already running a management system for ISO 27001 or ISO 9001? PRISM maps ISO 42001 onto it instead of requiring a parallel structure. The standard catalogue is activated on request at short notice — controls you already maintain are available to use immediately.
Why now
- • Enterprise customer or investor asking for a structured AI management system?
- • The EU AI Act requires governance evidence that ISO 42001 provides as a recognised framework?
- • Multiple AI systems in use but no central governance yet?
Organisations already running a management system have completed most of the work — processes, roles, document control — already. ISO 42001 then becomes an extension, not a new project.
What you concretely get
What PRISM brings for ISO 42001
-
AI management system controls to ISO/IEC 42001
Mapped onto your existing management system — no second system, no parallel documentation.
-
Gap analysis based on the existing engine
The engine already runs for ISO 27001, C5, SOC 2, NIS 2 and TISAX — your ISO 42001 catalogue is activated on request at short notice.
-
Multi-framework crosswalk
Controls already fulfilled under ISO 27001 or ISO 9001 are automatically reused for ISO 42001 — no duplication of effort.
-
AI assessment of your AI policies
PRISM reads your existing policies on AI roles and approval processes and shows per standard chapter what is missing.
-
Recognised building block for the EU AI Act
ISO 42001 structures AI governance obligations in a verifiable way — full AI Act crosswalk in preparation.
-
Internal audit & continuous improvement
Management review and continuous improvement directly in the platform — documented in an audit-proof manner.
No management system yet? Start with ISO 27001 — ISO 42001 can be mapped on top later.
AI Management System
ISO 42001 — your AI management system based on existing controls.
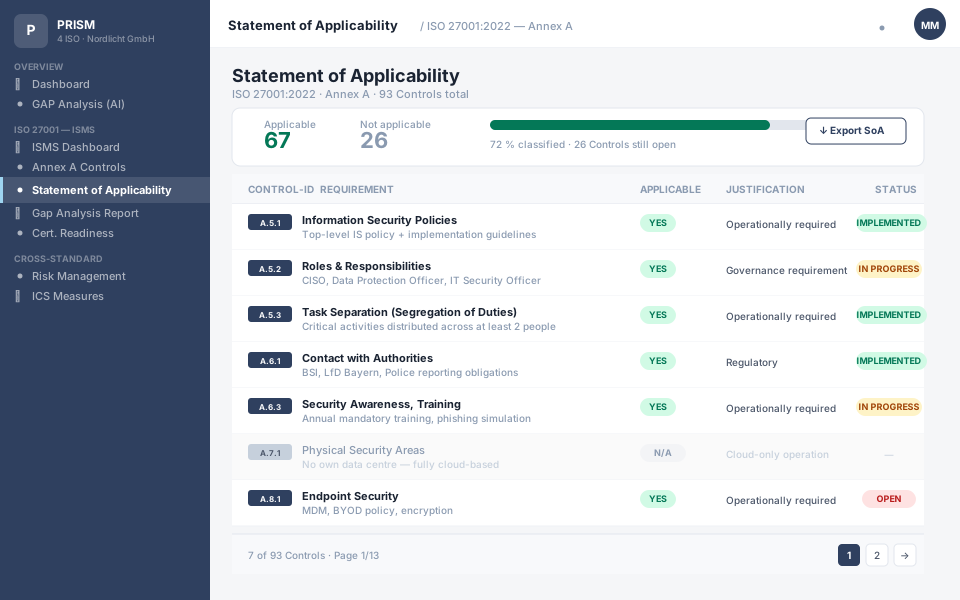
ISO 42001 is the first international standard for AI management systems. PRISM ISO maps AIMS requirements onto your existing management system and automatically creates a Statement of Applicability for AI-specific controls.
Who is this for?
Yes, if
- ISO 27001 or ISO 9001 already in use (with PRISM or elsewhere)
- One or more AI systems are developed, operated or procured
- Trigger: EU AI Act obligations, tender requirements or enterprise security questionnaire
- Goal: certification without building a parallel structure
Not suited
- No management system in place yet (build ISO 27001 or ISO 9001 first)
- No own AI system use — the EU AI Act alone is then usually not relevant
- Enterprises with a dedicated AI governance tool already in place
Are you deploying AI systems that fall under the EU AI Act? Learn more about the AI Act with PRISM — ISO 42001 is the structured foundation for it.
Frequently asked questions about ISO/IEC 42001:2023
- What is ISO 42001?
- ISO/IEC 42001:2023 is the first international standard for AI management systems (AIMS). It sets requirements for the responsible development, deployment and management of AI systems — including risk classification, impact assessment, transparency and continuous improvement.
- Who is ISO 42001 relevant for?
- ISO 42001 is relevant for organisations that develop, deploy or operate AI systems and wish to demonstrate this in a structured way — to customers, regulators or in the context of the EU AI Act. High-risk AI developers can use ISO 42001 as evidence of AI Act conformity.
- How does ISO 42001 relate to the EU AI Act?
- ISO 42001 and the EU AI Act complement each other: the AI Act is regulatory mandatory (a regulation with fines). ISO 42001 is a voluntary certification standard. An ISO 42001 certification can serve as evidence of conformity with the AI Act, particularly for risk management system requirements and technical documentation. PRISM ISO includes the crosswalk.
- Do I need to build a new management system?
- No. ISO 42001 is based on the high-level structure and can be mapped onto an existing management system (ISO 27001, ISO 9001). PRISM ISO transfers controls automatically — organisations already running an ISMS will have fulfilled many AIMS requirements already.
- How long does ISO 42001 certification take?
- With a structured approach and an existing management system, organisations are typically certification-ready within 3–6 months. Without an existing management system, we recommend building ISO 27001 as a foundation first and then mapping ISO 42001 as an AIMS extension.
Software only — or with consultant and auditor?
Three tiers, one goal: your certificate. From the licence to the fixed-price package with auditor included.
So geht PRISM vor
Von der Lücke bis zum laufenden Betrieb.
Vier Phasen, eine Plattform — kein Wechsel zwischen Tools, keine Lücken zwischen Phasen.




Wo stehen Sie heute?
PRISM bewertet Ihre bestehenden Dokumente, Prozesse und Kontrollen gegen alle Anforderungen der ISO 42001. Jede Lücke kommt mit Begründung und direktem Link zur Maßnahme — kein manuelles Zusammensuchen.
Was unsere Kunden sagen
„Der Security Health Check war sehr effizient und zielführend und half uns, Transparenz zu schaffen."
Johannes Beier
IT-Leiter · B2B Medical
Security Health CheckTrusted by











Show us your existing system.
In the initial call we clarify concretely what additional steps are needed for ISO 42001 and how quickly the catalogue can be activated.