

ISO/IEC 27001:2022
An ISMS that truly fits your organisation.
PRISM does not build a one-size-fits-all ISMS. The platform captures your processes, assets and documents — evaluates them against the 70+ chapters of ISO/IEC 27001:2022 — and guides you from your starting point through to ongoing operations. The certificate comes at the end automatically.
Typical starting situation
A key customer or corporate procurement requires ISO 27001 as a supplier requirement. Internally there is no ISMS — only scattered documents, Excel spreadsheets and the desire to get this behind you as quickly as possible.
"That takes a year" — our customers are certified in in an average of 3 months.
"We're too small" — references range from 20–200 employees.
- 70+
- Standard chapters of ISO/IEC 27001:2022 fully covered
- Avg. 3 months
- typical project duration to certification readiness
- Multi-Framework
- C5, NIS 2, SOC 2 via crosswalk from ISO controls
- Hosted in Germany
- Software and data on German servers, GDPR-compliant
What PRISM delivers for ISO 27001
From analysis to ongoing operations.
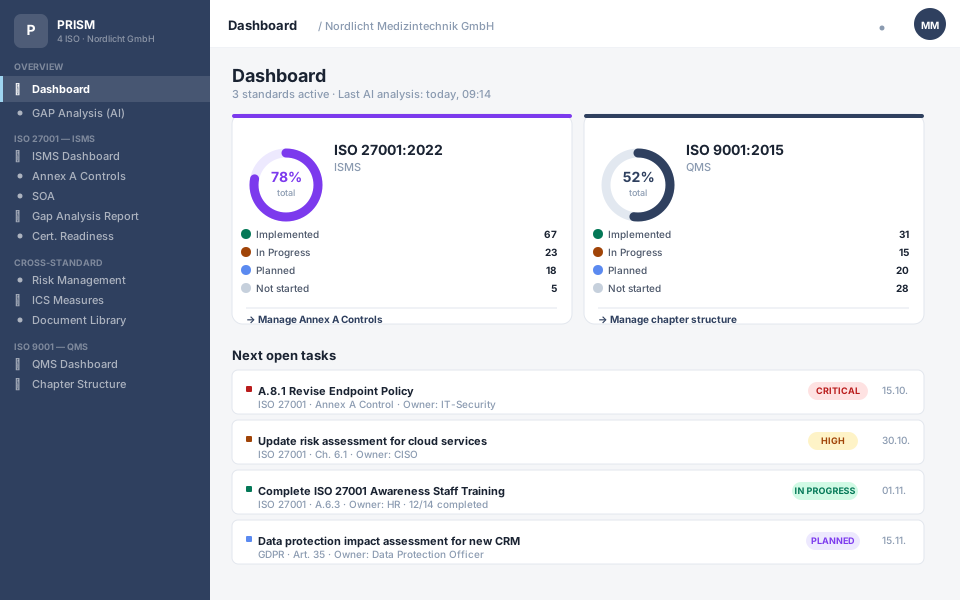
No switching between tools, no gaps between phases. Everything live in use.
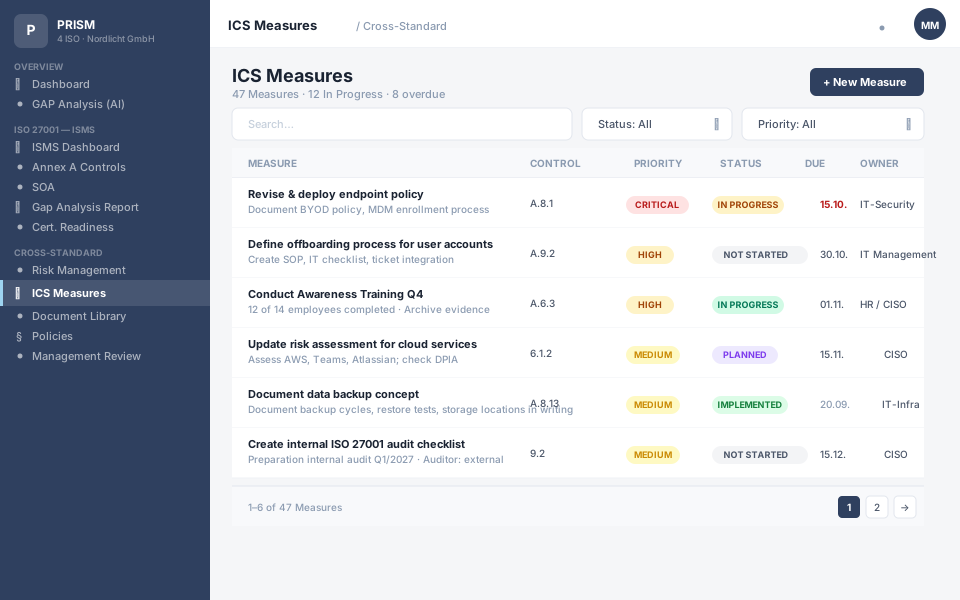
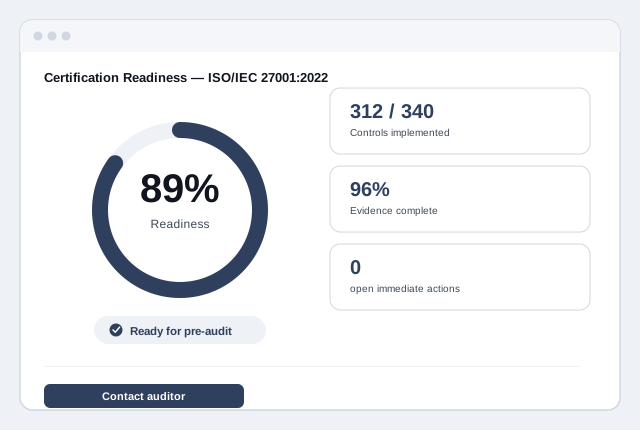
Analysis & Starting Point
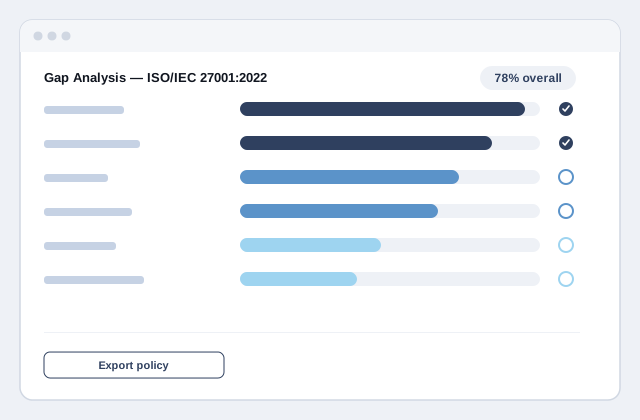
The AI evaluates your existing documents and processes against all 70+ standard chapters of ISO/IEC 27001:2022 — with a progress indicator per chapter and a concrete rationale for each gap. No manual searching required.
AI Policy Assessment
Every gap explained — per standard chapter.
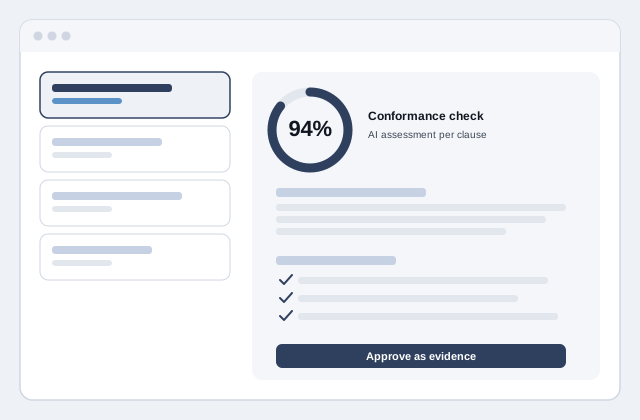
PRISM does not evaluate your policies against a generic checklist, but against the expectation horizon of each standard chapter — what an auditor actually checks. Gaps come with a rationale and a direct link to the action.
- Bulk analysis of entire document inventories at once
- AI score override with mandatory justification and audit trail
- Certification readiness dashboard — always current
How You Want to Work
Software alone — or with advisor and auditor.
Three tiers, one goal: your ISO 27001 certificate. What you need to do yourself is agreed upfront.
Self-Managed
Licence
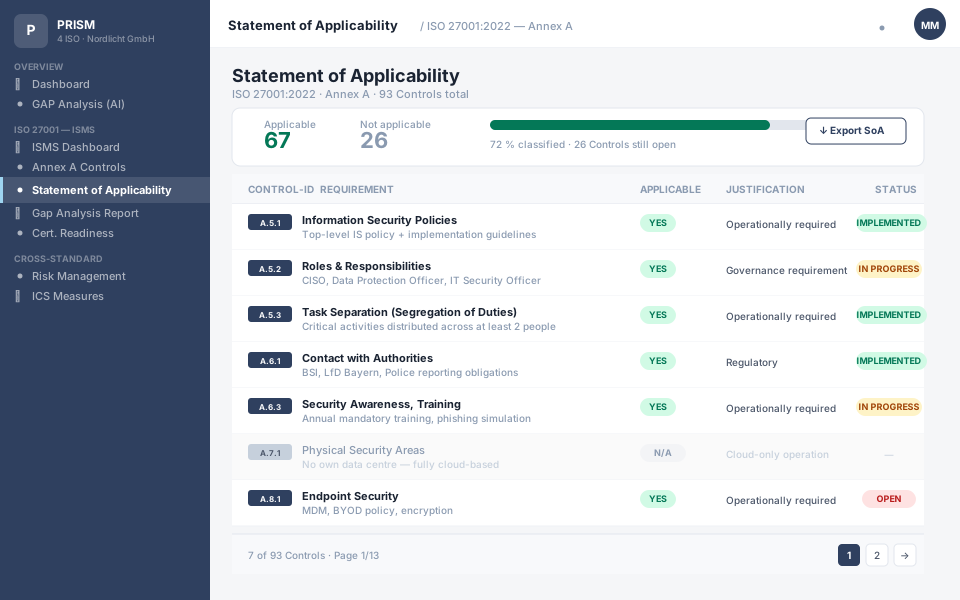
You work independently in PRISM ISO. Gap analysis, policy templates, AI assessment, SoA and action tracking — the platform guides you through all standard chapters. Ideal when compliance expertise exists internally or is to be built up.
- Complete PRISM ISO platform
- AI policy assessment included
- 80+ templates, all standard chapters
- Support via ticket
Guided
Software + Advisor
Our advisors work directly in your PRISM environment — SoA, policies, internal audits, management review. You provide the business specifics, we bring the standards expertise. Fixed price, fixed schedule.
- PRISM ISO platform
- Advisors with many ISO 27001 projects
- Guidance through to audit handover
- Fixed price instead of day rates
Certified
Software + Advisor + Auditor
The auditor is included from the start — with a fixed date and fixed price. No searching for a certification body, no price negotiation at the end. One contact, one target date, one price.
- PRISM ISO platform
- Advisor + independent auditor
- Fixed audit date from project start
- All-inclusive price — everything included
Was unsere Kunden sagen
„Die Zusammenarbeit mit Jürgen Kreuz und seinem Team ist stets sehr angenehm und erfrischend unkompliziert."
Jana Huhn
Projektmanagerin · HAUB+PARTNER GmbH
ISO 27001See PRISM with your own documents.
Bring a policy or your current status — in the initial consultation we show you what the AI makes of it.