

PRISM EagleEye · Security Operations
What is actually happening right now — not what was logged last week.
EagleEye combines security events from your SIEM/XDR, operational and capacity data from monitoring, asset dependencies on the OBASHI model, and threat intelligence (CISA-KEV/EPSS) into one situational picture — showing role-by-role which business processes are currently exposed to which risk.
The Problem
Security and compliance are separate worlds. For now.
SIEM without context
Your SIEM shows thousands of events — but not which business process is currently affected. Prioritisation by gut feeling.
Compliance without live data
Your ISMS shows where you stood at the last audit — not what is happening in your infrastructure today.
CMDB without connection
Assets are inventoried. But which asset supports which process, which requirement is affected? That link is missing.
How EagleEye works
What EagleEye does differently.
Three layers that have existed side by side — connected into one actionable situational picture.
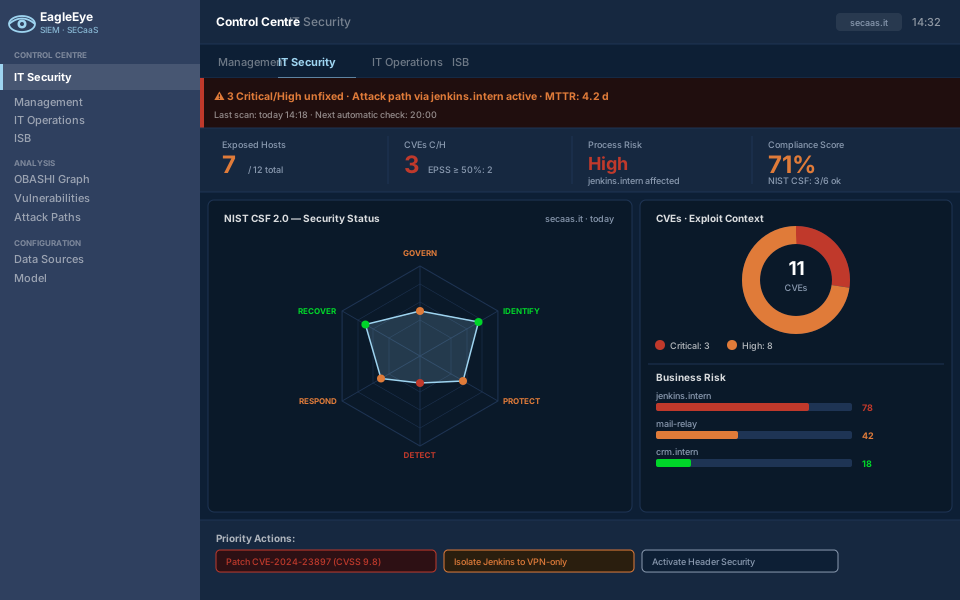
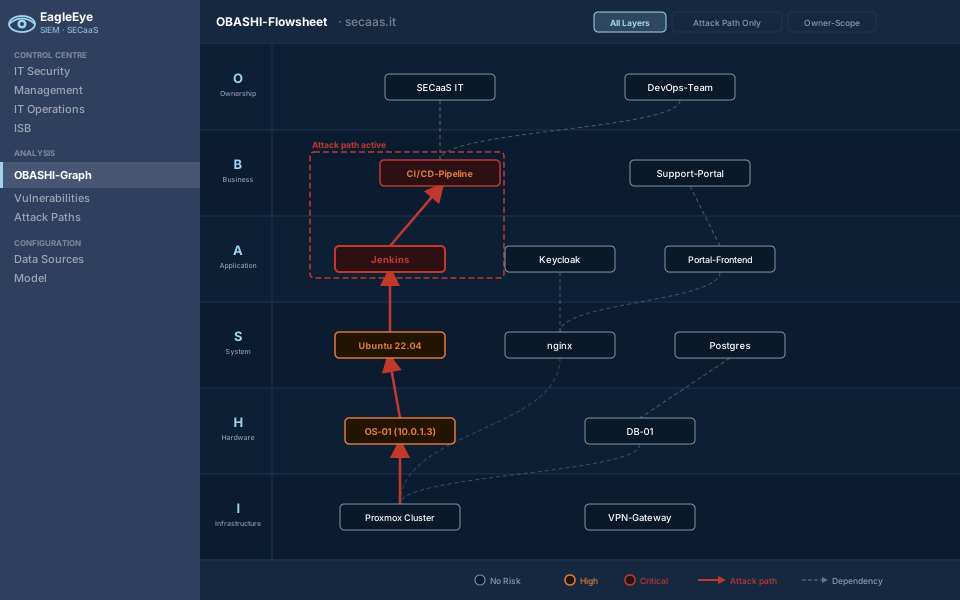
One picture instead of five tools
- Evidence from Wazuh/XDR, Zabbix monitoring, Docker version state and threat intelligence — continuously on a 5-minute cycle
- Asset dependencies on the OBASHI model (6 layers: Ownership, Business, Application, System, Hardware, Infrastructure)
- NIST CSF 2.0 radar, compliance score, exposed hosts and business risk — filtered by role for CISO, IT operations, ISB and management
Capabilities
More than a dashboard — an operational system.
ISO 27001 control mapping
Every SIEM event and every monitoring finding is automatically mapped to the relevant ISO 27001 control — audit evidence created by operations.
Regulatory crosswalk NIS-2 / DORA / KRITIS
Evidence and findings are also evaluated against NIS-2, DORA and KRITIS requirements — one event, multiple frameworks simultaneously.
CMDB reconciliation & asset drift
EagleEye detects when the actual infrastructure diverges from your CMDB — new assets, disappeared hosts, changed relationships.
Evidence-based copilot
AI-assisted analysis of findings with verifiable evidence links — no blackbox, every suggestion is traceable to source data.
Architecture, Operations & Maturity
Self-hosted, Made in Germany
Docker Compose deployment, non-root containers, TLS, VPN-only gate; data stored in Germany.
Lean, auditable core
Logic in a unit-tested stdlib core (render-only UI); SQLite today, PostgreSQL as target architecture.
Data sources
Wazuh/XDR, Zabbix, Docker versions, CISA-KEV/EPSS, CIS/SCA — extensible via a connector model.
Maturity
EagleEye Core v1.0 is production-ready and runs as our own operations and security centre — available for customer environments now.
One system for Security Operations and Compliance.
PRISM ISO shows where your organisation should be. PRISM Audit checks whether it is there. EagleEye shows what is happening right now.
| PRISM ISO | PRISM Audit | EagleEye | |
|---|---|---|---|
| Shows | Where you should be | Whether you comply | What is happening now |
| Time perspective | Certification cycle | Audit year | Continuously (5-min cycle) |
| Audience | ISMS team / management | Auditors / revision | CISO / IT ops / ISB |
| Key question | Do we have all controls? | Do we maintain them? | Are we secure right now? |
See EagleEye on a real situational picture.
In the initial consultation we show how SIEM/XDR events, asset dependencies and compliance evidence come together in an actionable situational picture. No pitch — we clarify whether EagleEye fits your security infrastructure.