

For critical infrastructure operators
Clinics, auditors and critical infrastructure operators already manage their evidence in PRISM.
§75c SGB V, B3S audit cycles and limited resources: when evidence must be consolidated across multiple sites without knowledge walking out the door with every consulting project, this is our reference home turf.
Typical situation
- • Upcoming audit date (BSI/DKG)
- • Carrier merger — new sites need to be integrated
- • Security incident in the sector increases pressure
"Our environment is special" — multiple clinics and critical infrastructure operators already use PRISM (see logos below). "Data protection with cloud software?" — server and AI processing in Germany, DPA, on-premise option possible.
In use at, among others


What PRISM relies on today
The ISO 27001 foundation of PRISM ISO covers the core requirements for an information security management system — a standalone B3S audit catalogue module is in preparation. Until then, our critical infrastructure references work with the existing ISO 27001 tooling.
Critical Infrastructure Evidence
§8a BSIG — Evidence every 2 years, without the rush.
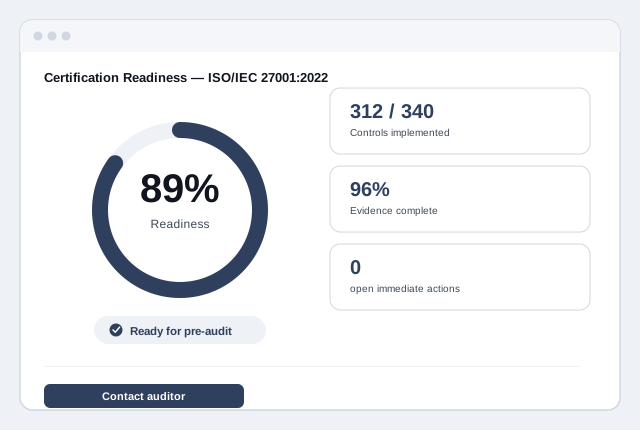
Critical infrastructure operators must demonstrate to the BSI every two years that they have taken appropriate measures to secure critical infrastructure. PRISM ISO structures the B3S requirements and keeps the evidence continuously up to date.
Who is this for?
Good fit
- ✓ Critical infrastructure operators with §8a BSIG evidence obligations
- ✓ Hospitals and hospital groups (§75c SGB V)
- ✓ Carriers with multiple sites needing to consolidate evidence
- ✓ Information security officers with an upcoming BSI or DKG audit
- ✓ Organisations with an existing ISO 27001 foundation looking to add B3S
Less suitable
- ✗ Companies below BSI threshold values without evidence obligations
- ✗ Single-site organisations without multi-framework requirements
- ✗ Looking for a pure document storage system without an audit trail
Frequently asked questions about critical infrastructure / B3S
- What is critical infrastructure and who is affected?
- Critical infrastructure refers to facilities, systems and installations whose failure would have significant consequences for public services. Operators in the sectors of energy, water, food, IT & telecommunications, healthcare, transport, finance and public administration are affected when they exceed the BSI threshold values (typically: ≥ 500,000 people served).
- What must I demonstrate as a critical infrastructure operator?
- Under §8a BSIG, critical infrastructure operators must demonstrate to the BSI every two years that they have taken "appropriate organisational and technical precautions" in line with the state of the art. This is done through evidence, audits or certifications following the sector-specific security standards (B3S) of the relevant sector.
- What is a B3S and how does it differ from ISO 27001?
- A sector-specific security standard (B3S) is a sector-specific guideline recognised by the BSI — for example for healthcare, water supply or energy. B3S requirements overlap significantly with ISO 27001 but go further in some areas (e.g. operational continuity, redundancy). PRISM ISO covers both.
- How frequently must evidence be provided?
- The evidence cycle under §8a BSIG is two years. The BSI has the right to order additional audits. With PRISM ISO, evidence is kept continuously up to date — the complete documentation and change history are available to the BSI at any time, with no last-minute effort required.
- Can I cover critical infrastructure and ISO 27001 together?
- Yes. ISO 27001 frequently forms the basis for the critical infrastructure evidence — many B3S requirements are identical. PRISM ISO provides the multi-framework crosswalk: ISO 27001 controls are automatically mapped to B3S requirements. Our team has references in the healthcare sector (§393 SGB V / §8a BSIG).
Software alone — or with a consultant and auditor?
Three tiers, one goal: your critical infrastructure / B3S evidence. From licence only to a fixed-price package with auditor included.
Was unsere Kunden sagen
„Der Security Health Check war sehr effizient und zielführend und half uns, Transparenz zu schaffen."
Johannes Beier
IT-Leiter · B2B Medical
Security Health CheckTrusted by









Shall we show you a critical infrastructure setup from your sector?
In the initial call — tailored to your carrier structure.