

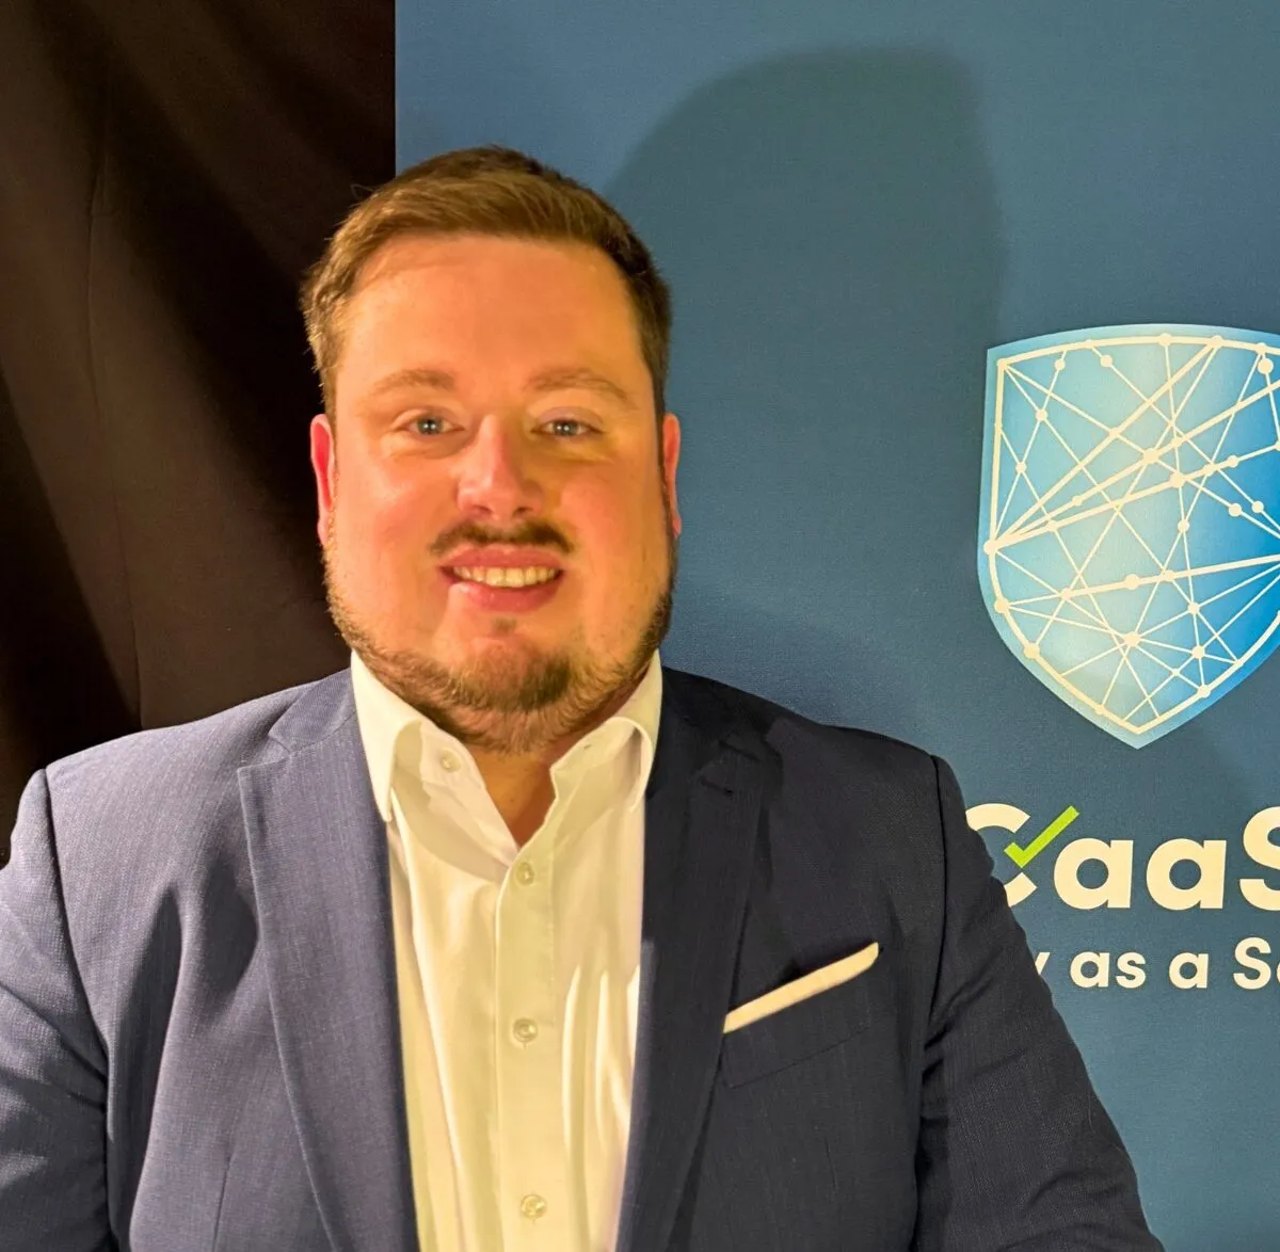
Jörg Spöcker
CEO
Responsible for operations and the strategic development of SECaaS.IT. Jörg makes sure the company delivers what it promises — structured, reliable, and without surprises.
About SECaaS.IT
SECaaS.IT is not a provider of forms and checklists — we permanently change how organisations implement and operate information security. Software, consulting and a directly bookable auditor, all from one source, at a fixed price.
Trusted by











Our approach
Regulators across Europe are making the same demand: ISO 27001, NIS 2, DORA, the AI Act and the CRA do not ask for a certificate. They ask for a living, auditable information security management system — one that operates continuously, adapts to new threats, and produces evidence on demand. The BSI is moving in exactly this direction with its integrated, risk-based approach to IT-Grundschutz. We built PRISM for exactly this reality.
01
Structured implementation
PRISM guides your team through the complete implementation — SoA, policies, controls, risk assessment. Knowledge stays in-house; no consultant dependency after go-live.
02
Continuous operation
After certification, PRISM keeps your ISMS alive: automated evidence collection, ongoing control testing, regulatory change monitoring — all documented and audit-ready.
03
Multi-framework coverage
One platform, 14+ frameworks. ISO 27001, BSI C5, NIS 2, DORA, AI Act, CRA, TISAX, SOC 2 — regulations build on each other. PRISM maps the overlaps: implement once, satisfy many.
The compliance platform that covers the complete lifecycle — from day one to every re-certification.
Most providers help you get certified. Few help you stay certified. Software, consulting and a directly bookable auditor in a single fixed-price offering — that is our concrete proposition. It addresses the direction both the BSI and the European regulatory framework are moving: compliance not as an event, but as a permanent operational capability.
The team
Jörg Spöcker
CEO
Responsible for operations and the strategic development of SECaaS.IT. Jörg makes sure the company delivers what it promises — structured, reliable, and without surprises.
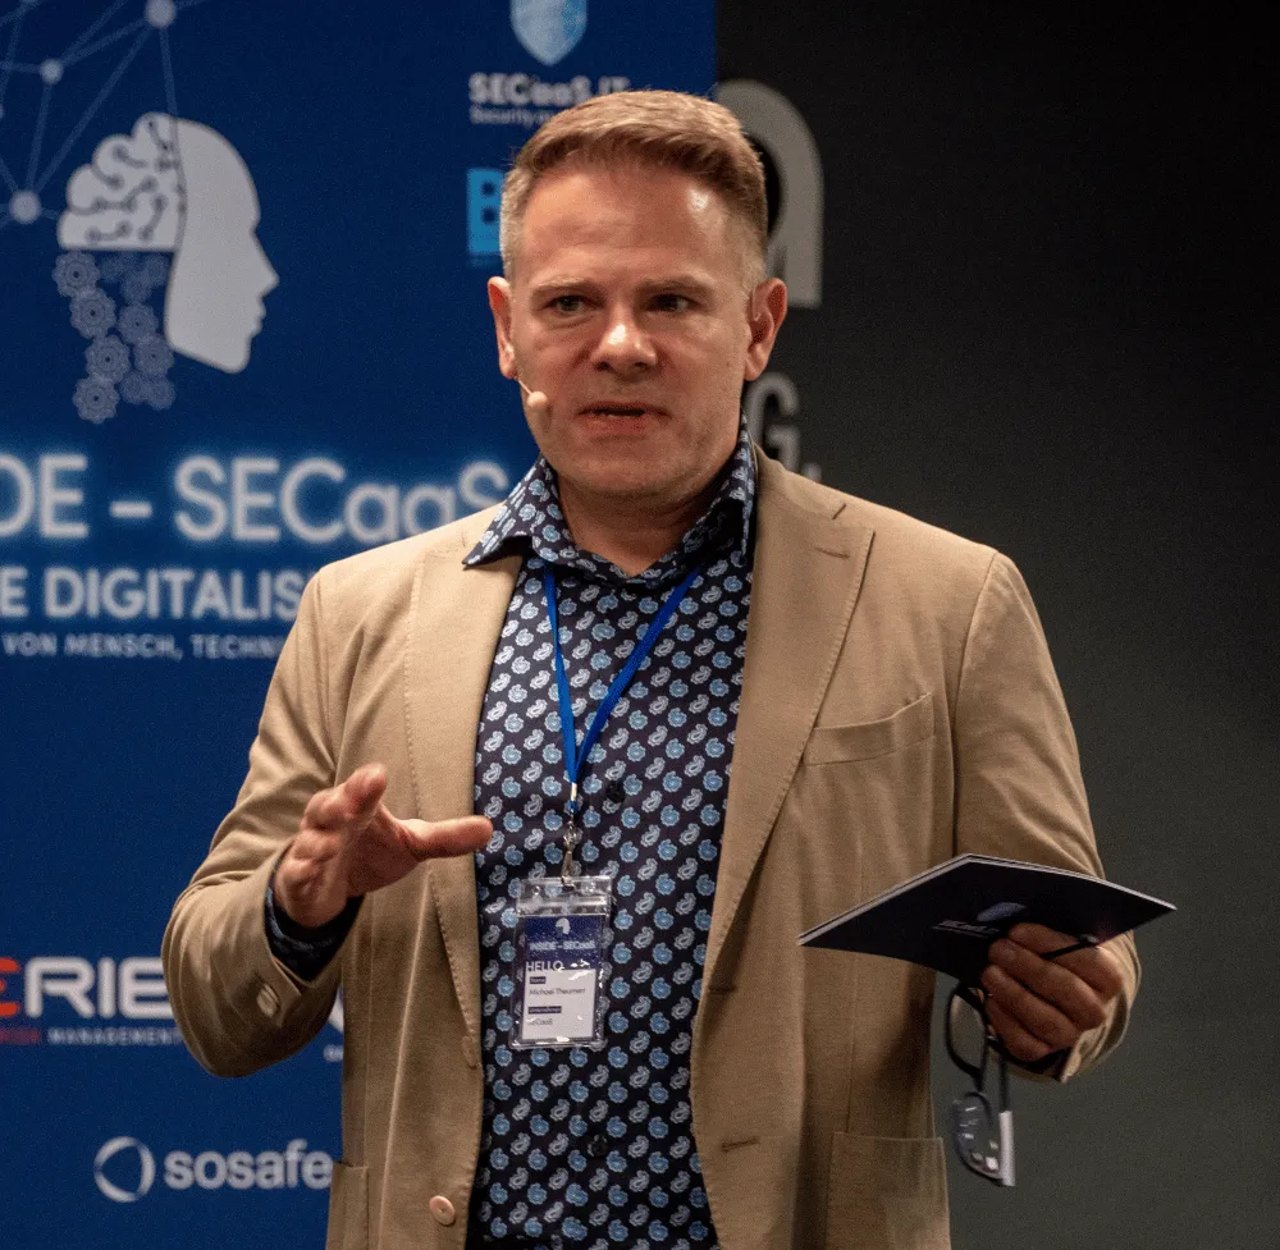
Michael Theumert
Co-Founder
Co-founder and technical mind behind the early SECaaS product philosophy. Michael laid the methodological foundation for what runs in PRISM today.
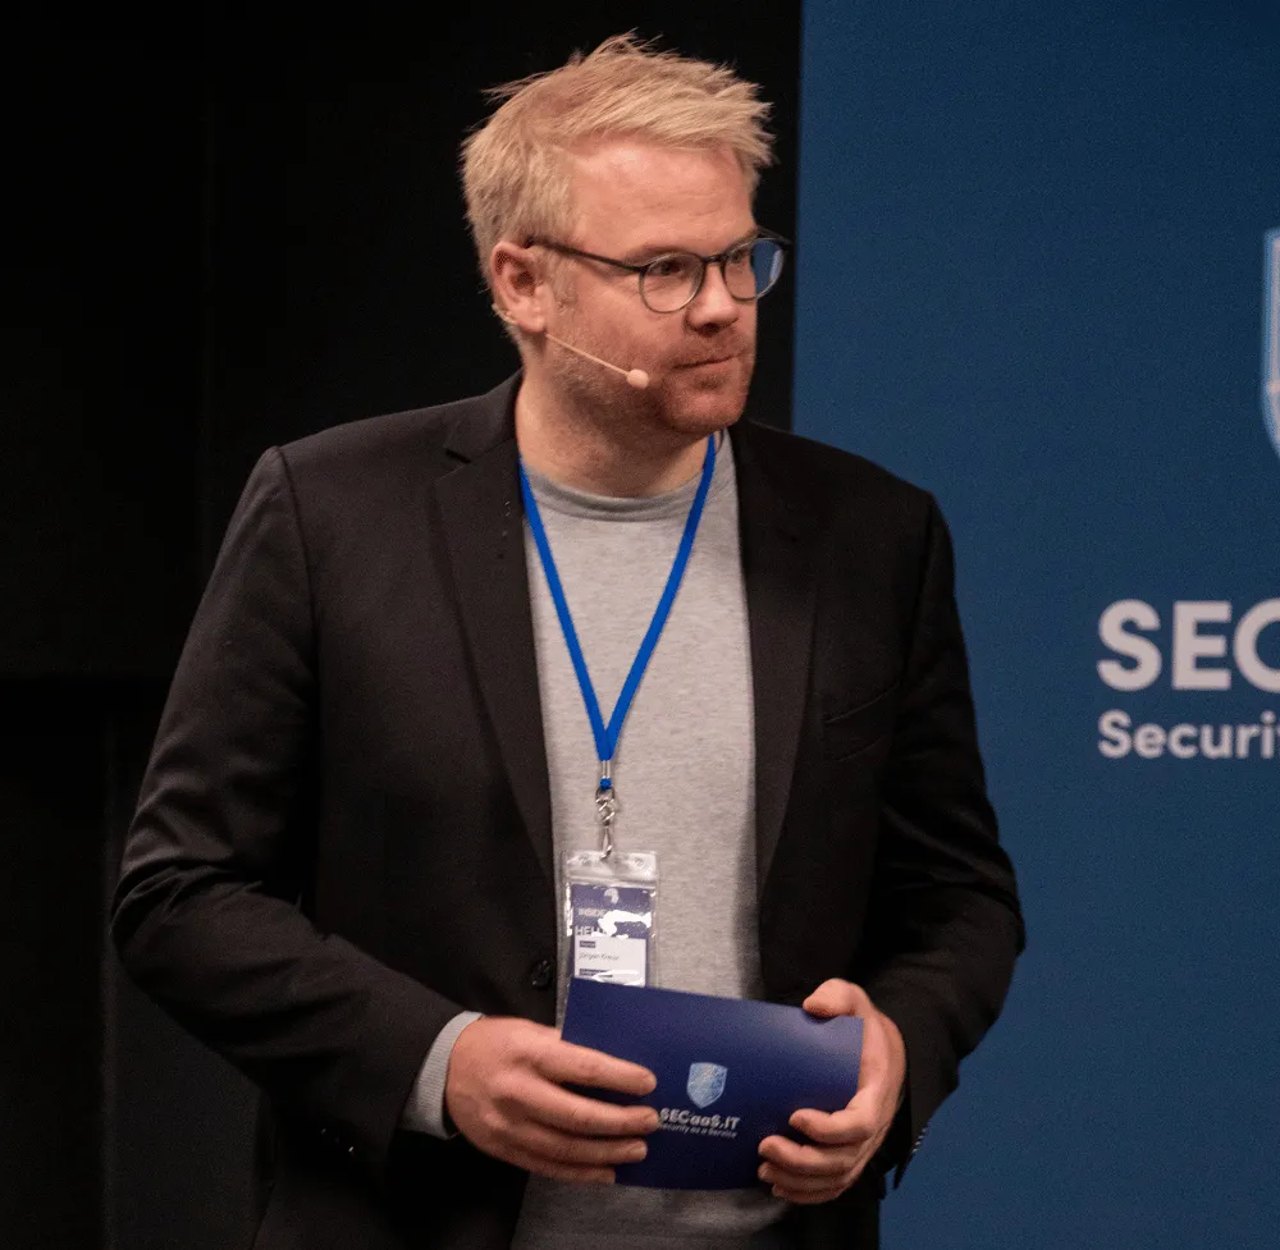
Jürgen Kreuz
Co-Founder
Co-founder of SECaaS.IT and architect of the PRISM platform. Jürgen combines hands-on experience from hundreds of implementation projects with a talent for structural scaling — from the first policy to enterprise certification.
Memberships & Appointments
EU Health Cybersecurity Advisory Board · European Commission
Jürgen Kreuz was appointed to the Health Cybersecurity Advisory Board of the European Commission in 2025 — one of the few German members of this EU advisory body for cybersecurity in the healthcare sector.
Bundeswirtschaftssenat · BVMW — wirtschaftssenat.de
In recognition of entrepreneurial achievement, Jürgen Kreuz was appointed to the Bundeswirtschaftssenat of the BVMW in 2024 — the excellence committee of Germany's federal association for medium-sized businesses.
Network
For specialist areas we work with selected partners — vetted, coordinated with each other, and proven in joint projects.
 Audit & Certification
TASCO Revision und Beratung GmbH
Objective audit and advisory services for mid-market companies — from IT audits and compliance consulting to the establishment of internal audit functions. Certified to DIIR Audit Standard No. 3.
tasco-revision.de → Consulting & Transformation
LeadingSecure GmbH
Specialist security layer for mid-market organisations — governance, resilience and accountability as external ISB and vCISO. ISO/IEC 27001, NIS-2, BCM to BSI 200-4.
leadingsecure.de → Audit & Certification BFMT Gruppe
Independent auditors and IT auditors (SSAE 18). BFMT is our preferred audit partner for BSI C5 and ISO certifications across the German-speaking region.
bfmt.net → Audit & Certification Ypsilon Wirtschaftsprüfer
Specialist audit firm focused on IT compliance and cloud attestations. Uses PRISM Audit for its own audit work.
ypsilon.group → Audit & Certification
Advanta Wirtschaftsprüfung
Audit and assurance specialists for IT-intensive organisations. Partner for ISO and BSI C5 attestations in complex regulatory environments.
advanta.de → Consulting & Transformation
e-brain Solutions
Specialists in IT governance, risk and compliance consulting. Long-standing partner for cross-sector ISMS implementation projects.
ebrain-solutions.de → Technology & Development
U-KNOW
Technology and development partner for custom AI solutions — CRM/ERP integration, automation, chatbots and AI agents.
u-know.ai → Consulting & Transformation
Ontron GmbH
Process optimisation and IT project management since 1999, specialising in hospitals and administrative organisations. Structured approach to digitalisation and efficiency gains.
ontron.de → Audit & Certification
Collegium Auditores GmbH
Specialised in IT audit, compliance, data protection and information security. Supports organisations with NIS-2/BSIG implementation and AI governance.
collegium-auditores.com →Are you a consultant, MSP or auditor?
PRISM is available as a white-label and co-branding solution for partner organisations. Join our network and offer your clients Compliance as a Service.
Enquire about partnershipContact
Sebastian-Kneipp-Straße 41
60439 Frankfurt am Main
In the initial call we show how we work concretely for your organisation — no sales pitch.